- Solutions
- Pricing
Key Takeaways:
A true enterprise AI app builder never trains its underlying models on your proprietary data. Employees often assume all artificial intelligence works exactly like public chatbots. These consumer tools ingest user inputs to get smarter, and this assumption stalls digital transformation projects because IT teams fear severe data leaks. That fear is completely justified.
According to a 2025 report by Gartner, more than 40 percent of AI-related data breaches will be caused by the improper use of generative AI by 2027. Business process automation requires a completely different technical architecture. An AI-powered no-code platform uses artificial intelligence to route tasks and build workflows, but it treats your operational records as highly restricted information.
Proper AI app builder data privacy ensures that your confidential records remain isolated from the reasoning engine. Understanding exactly how data moves through an automation platform is the only way to evaluate enterprise AI security accurately.
AI platforms consume data in two distinct ways. They either ingest it permanently to train the model, or they reference it temporarily to generate a single response. The mechanical difference between a model learning from data and a model simply reading a prompt dictates your entire operational risk profile.
Model training means the artificial intelligence permanently absorbs the information. This absorption alters its underlying neural network and makes your operational inputs part of its future baseline knowledge. Real-time processing operates on a completely different architecture. It means the artificial intelligence reads the data to answer a specific query, provides an immediate output, and forgets the input entirely once the task concludes.
This technical distinction is critical because employees frequently misunderstand how different systems handle sensitive records. According to a 2025 report by Gartner, 75% of organizations running generative AI initiatives will reprioritize their data security efforts by 2026 specifically to manage new exposure vectors caused by training-active models.
Enterprise platforms achieve secure real-time processing through Retrieval-Augmented Generation, commonly known as RAG. RAG allows an artificial intelligence engine to search your internal database for an answer without actually learning or memorizing your proprietary records.
When an employee asks a question, the system retrieves the most relevant documents from your secure storage. It then hands them to the processing engine alongside the original prompt so that the system can generate a relevant answer. The model reads those specific documents, drafts an accurate answer, and immediately discards the context once the session ends.
Because your operational database remains separated from any AI model training data, your workflows remain automated without violating your internal AI data usage policy. This architecture ensures that secure AI applications can route tasks and build internal tools without exposing your business data.
{CTA button: Book a Demo:https://www.codeblox.com/schedule-demo:Ready to build automated workflows on a secure architecture your IT team will actually approve? Book a walkthrough and watch how your first secure process gets built. }
Using an automation platform with a weak AI data usage policy exposes your company to immediate intellectual property loss and severe compliance violations. Legacy ERP modernization requires migrating highly sensitive information like bills of materials, supplier contracts, and pricing structures into new cloud environments.
This transition creates significant vulnerability if the chosen automation tool does not isolate your operational records properly. If the AI platform data privacy rules are loose, your secure data simply becomes part of the vendor's massive machine learning ecosystem. Your operations team might gain faster internal workflows, but they do so at the unacceptable cost of losing ownership over core business assets.
When a model absorbs your business data, it permanently blends your proprietary methods into its broader reasoning capabilities. A direct competitor using the exact same software platform could potentially prompt the system about supply chain optimizations and receive outputs heavily influenced by your internal workflows.
This invisible leakage destroys competitive advantage instantly without anyone ever hacking your corporate servers. Because of this specific threat, strict data confidentiality in AI is non-negotiable for manufacturing and finance sectors. These industries rely heavily on closely guarded operational secrets to maintain their market position, and they cannot afford to train a vendor's algorithm for free.
Regulatory frameworks like GDPR, HIPAA, and SOC 2 require companies to know exactly where their customer and operational information lives at all times. If a generative model absorbs your records during a routine task, you lose the ability to track or delete that specific information on demand.
You can no longer prove to an external auditor that you maintain full control over your systems, which leads directly to failed compliance checks and substantial financial penalties. Strong AI compliance and security means you must always retain the technical power to locate, isolate, and wipe every single record your business owns.
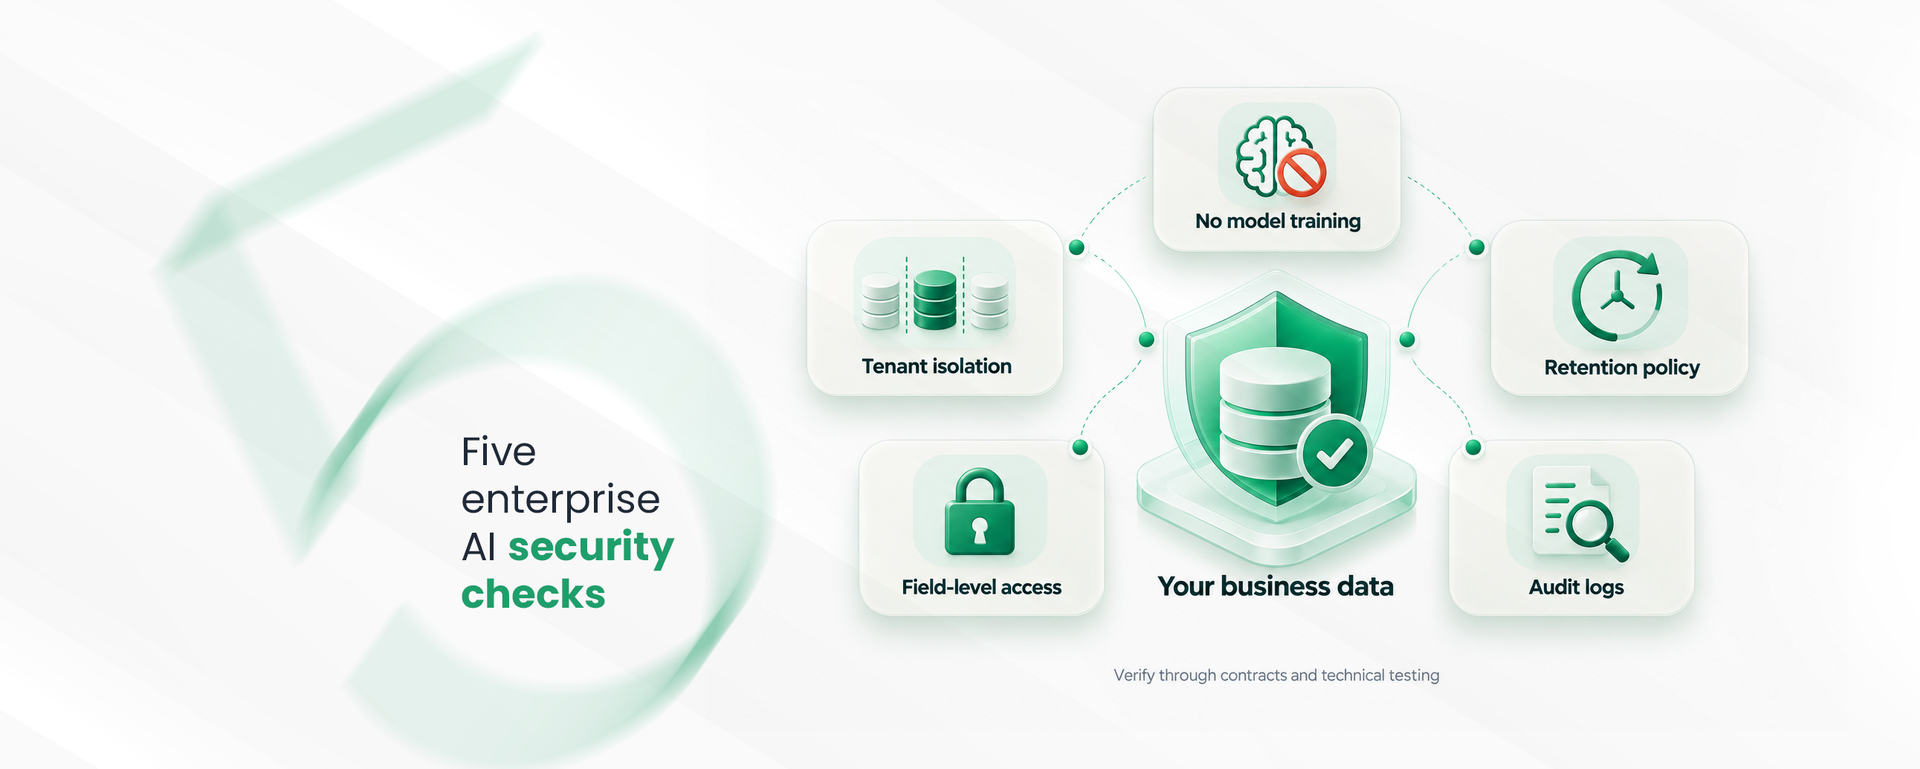
True enterprise AI security is defined by zero data retention policies and strict tenant isolation. You should never settle for vague vendor promises about data safety. An AI app builder data privacy policy must mathematically and contractually prove it cannot access your operational records under any circumstances.
IT leaders must verify these structural boundaries before moving a single internal workflow into a new environment. According to Gartner's 2026 AI Risk Management overview, 80 percent of CIOs now require explicit zero-retention API clauses before authorizing any new workflow automation platform.
This strict procurement standard forces software providers to build actual walls around your information. It shifts the burden of proof onto the vendor to demonstrate exactly how their AI platform security operates at the database level.
A zero-retention API guarantees that the artificial intelligence provider does not log, store, or learn from the prompts sent to it. When an employee queries the system, the model processes the request and instantly drops the payload. This mechanism means no trace of your query exists on the vendor's servers after the task finishes.
This architectural choice allows teams to use artificial intelligence for auto-classification and smart routing without creating a permanent data trail. You get all the speed benefits of automated task management, and you avoid the long-term liability of exposing sensitive financial records to a third-party reasoning engine. Strong AI app data security always depends on this immediate disposal of processed information.
This disposal mechanism works alongside robust tenant isolation to completely seal your operational environment. Tenant isolation ensures that your database, your workflows, and your AI queries sit in a secure, fenced-off space that no other customer can access. The infrastructure logically separates your tenant from every other company using the same cloud provider.
This setup prevents cross-contamination between different organizations running on the same underlying software. Your business data protection remains absolute even on a massive shared cloud platform because the architecture blocks data from bleeding across tenant borders. You maintain total authority over your operational assets while still leveraging modern automation capabilities.
You audit an AI platform by examining its data processing agreements and testing its role-based access controls. IT leaders must verify vendor claims before migrating any core systems into a new environment. A software provider might market their tool as a fast, no-code solution.
However, the underlying database structure ultimately determines if the platform is actually safe, which is why operations directors must inspect the technical foundation. Strong AI data governance requires you to look past the user interface and examine how information actually moves.
The first step of this audit involves evaluating the vendor contracts and API connections. You need to look for specific clauses that explicitly opt your company out of data sharing. The legal agreement must state clearly that your inputs will never be used for model training. If an AI software security policy is buried in a dense document or difficult to understand, it is likely written to protect the vendor rather than the customer.
Transparent documentation is a baseline requirement for legitimate AI data protection. Procurement teams should reject any platform that refuses to provide straight answers about their data routing practices.
After clearing the legal terms, you must test the internal access controls. An automated assistant is exactly as secure as the specific user prompting it. The AI integration must inherit field-level permissions directly from the database, ensuring that the model strictly respects your existing corporate hierarchy.
Consider a scenario where a junior employee asks the assistant to summarize upcoming departmental budget cuts. If that employee lacks authorization to view financial records in the standard database, the AI must block them from asking questions about those specific records. Testing these rigid internal boundaries confirms that your chosen system enforces true data confidentiality in AI interactions across your entire organization.
CodeBlox explicitly blocks all customer data from being used as AI model training data to ensure total privacy for your operations. The platform acts as an operating system for your entire business.
It drafts workflows, builds forms, and routes approvals using artificial intelligence, but it never absorbs your proprietary data into its foundation. This architectural choice provides the exact AI platform security that IT leaders require before migrating core processes.
The platform runs directly on Microsoft Azure. This infrastructure provides enterprise-grade security, disaster recovery, and regional data residency natively. These built-in features keep the system compliant with strict regulatory frameworks. Your operations team can deploy secure ai applications without constantly worrying about underlying server vulnerabilities or hardware maintenance.
CodeBlox applies access permissions at the exact field level. The artificial intelligence engine actively reads these rules and strictly respects your established boundaries. It immediately stops unauthorized users from extracting data, keeping all your internal apps fully governed. A junior representative cannot use the smart assistant to bypass system rules and access restricted executive dashboards. This deep integration ensures complete customer data protection across every single department.
Modernizing your operations does not require sacrificing your AI app builder data privacy. The clear distinction between a smart spreadsheet and a governed enterprise platform lies entirely in how they handle data.
As process automation becomes a standard practice, companies that establish strict boundaries now will scale much faster than those fixing data leaks later. You need to stop relying on fractured legacy systems and shadow tools. Move your operations to a governed platform where IT maintains complete visibility and business teams can build safely.
Making this operational shift requires a software vendor that treats your enterprise AI security as a foundational rule rather than a premium feature. You must choose a platform that proves its technical commitment to keeping your digital borders closed.
CodeBlox delivers unmatched expertise in AI platform data privacy by physically separating your internal records from all reasoning engines. The system guarantees that your daily workflows remain fully automated while your enterprise AI security stays perfectly intact.
{CTA button: Book a Consultation:https://www.codeblox.com/schedule-demo:Take control of your operations and safely modernize your legacy systems with CodeBlox. Move to a governed platform where your business teams can build without sacrificing data privacy. }
Find answers to the most common questions about our no-code platform and how it can help you build powerful business application solutions without writing a single line of code.
Organizations ensure data confidentiality in AI by selecting workflow platforms that offer mathematically proven, zero-retention API agreements. Deploying these secure AI applications on governed infrastructure like Microsoft Azure physically blocks unauthorized cross-tenant data contamination.
AI data governance involves implementing strict access controls that dictate exactly how artificial intelligence interacts with your internal database. This framework forces the AI assistant to inherit existing field-level permissions, preventing unauthorized employees from accessing restricted operational records.
Enterprise AI security operates on a zero-retention architecture, unlike standard consumer tools that actively harvest prompts for continuous learning. This strict tenant isolation ensures that your proprietary business data protection remains absolute across shared cloud infrastructures.
Secure enterprise AI platforms never ingest or use your proprietary customer data to train their foundational machine learning algorithms. These systems process your prompt to generate a real-time response and immediately discard the information to maintain strict compliance.
AI app builder data privacy guarantees that your proprietary business workflows remain completely isolated from underlying machine learning engines. This architecture prevents vendors from using your confidential financial records or operational prompts as AI model training data.
Chris has spent more than a decade designing and delivering enterprise software for organizations with complex operational requirements. Drawing from real implementation experience, he writes about enterprise architecture, CRM strategy, digital transformation, software modernization, and the challenges organizations face when scaling business operations.