- Solutions
- Pricing
AI app builders let a clinic or health startup build an intake form, a referral tracker, or a patient follow-up tool in a day. The next question is whether that app can safely hold patient data.
The answer depends on more than the app itself. HIPAA compliant AI apps need a compliant platform, a signed BAA with every vendor that touches patient data, and controls that your team actually uses. This guide covers what to check before an AI-built app handles real patient information.
An AI app is HIPAA compliant when it protects patient data according to the HIPAA Privacy Rule and Security Rule, and every vendor in the chain has signed a BAA. There is no government certificate for this. HHS does not certify software, so a "HIPAA certified" badge on a website is a marketing claim, not an official status.
HIPAA applies to two groups:
Protected Health Information (PHI) is any health information that can identify a person. Names, dates, phone numbers, email addresses, and medical record numbers all count when they are linked to health data.
The HIPAA Security Rule sets the safeguards for electronic PHI. It groups them into administrative safeguards like risk analysis and staff training, physical safeguards like device and facility controls, and technical safeguards like access control, audit logs, and encryption.
HIPAA compliant software is software that can be set up and used in a way that meets these rules. The same tool can be compliant in one setup and non-compliant in another.
AI-built apps follow the same rules as any other software. They also create new places where patient data can end up, and most of those places sit behind the screens users see. That makes healthcare data security harder to check by looking at the app alone.
Common risk points include:
For AI data privacy, map where patient data travels and confirm that every stop is covered.
HIPAA-compliant app development starts before the first screen is built. Use this checklist before an AI-built app stores or processes real patient data. The first six checks cover the platform and infrastructure. The next six cover the AI features.
Get a signed Business Associate Agreement (BAA) from the app platform, the cloud host, and any AI model provider that receives PHI. If a vendor will not sign one, do not send it PHI.
Confirm the app runs on HIPAA-compliant cloud services covered by a BAA. Major cloud providers publish lists of HIPAA-eligible services, so check that every service your app uses is on that list.
All PHI should be encrypted when it is stored and when it is sent. Ask which encryption standards the platform uses and who manages the keys.
Each user should see only the patient data their role needs. Strong healthcare data access controls limit records by role, team, or location and remove access quickly when someone leaves.
Require MFA for every user who can access PHI. HHS's proposed Security Rule update would make it mandatory, and many cyber insurers already expect it.
The app should record who viewed, created, changed, or exported each patient record and when. Logs should be protected from editing and kept for your full retention period.
{CTA button:Start building free:https://www.codeblox.com/sign-up:Build healthcare apps with role-based access and audit trails from day one.}
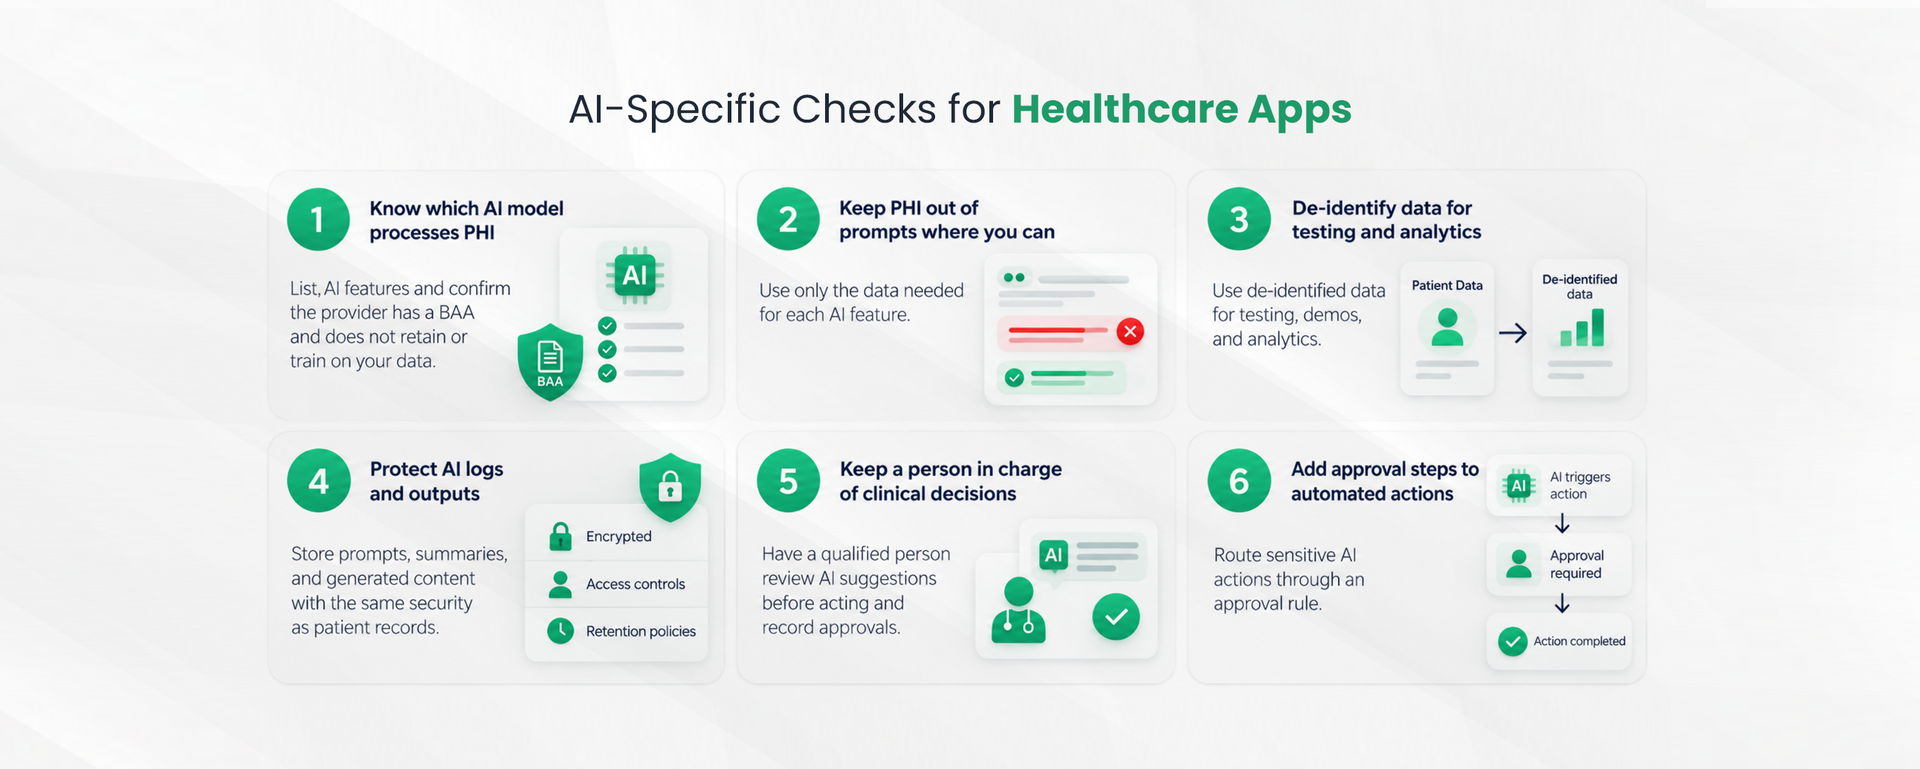
These checks protect patient data privacy in the areas that traditional software reviews often miss.
List every AI feature in the app and the model provider behind it. Confirm that each provider has signed a BAA and does not keep or train on your data.
Design AI features to use only the data they need. A scheduling assistant may need a date and a clinic location, not a diagnosis.
Use de-identified data for testing, demos, and analytics. HIPAA recognizes two methods: removing 18 specific identifiers or getting an expert to confirm that the risk of re-identifying anyone is very small.
Treat prompt logs, summaries, and generated documents as PHI. Store them with the same encryption, access rules, and retention policies as patient records.
AI suggestions that affect patient care should be reviewed by a qualified person before anyone acts on them. Record who approved what.
When AI triggers actions such as sending reminders or updating records, it routes sensitive steps through an approval rule. AI workflow automation with built-in approvals and logging keeps healthcare application development fast without skipping checks.
The HIPAA Security Rule already requires a risk analysis. An AI risk assessment extends that analysis to cover how AI features use, store, and share patient data.
A practical AI risk assessment answers these questions:
AI governance in healthcare means having clear rules for which AI tools staff may use, who approves new AI features, and how problems are reported. Even a small clinic benefits from a one-page AI policy and a named owner.
Healthcare software compliance is ongoing work. Each new feature, integration, or vendor should go through the same review before it touches patient data.
Before choosing a platform, ask for written answers to these questions:
If a vendor cannot answer clearly, treat that as a warning sign. Teams building HIPAA-ready AI applications should have these answers in hand before any patient data goes into the system.
No. A compliant platform and HIPAA compliant cloud services give you the right foundation, and your organization is still responsible for how the app is set up and used.
Your team still needs to:
Healthcare cybersecurity also goes beyond HIPAA. State privacy laws may add their own rules, especially for apps that serve patients in several states.
HHS proposed a major update to the Security Rule in January 2025. It would make encryption, MFA, and regular vulnerability testing mandatory. As of October 2026, the update is still not final, and HHS now targets July 2027 for final action, so the current Security Rule remains in force. Building to the proposed standard now means less rework if it is finalized.
AI-built apps let healthcare teams launch tools in days. With patient data involved, the setup matters as much as the speed. HIPAA compliant AI apps rely on vendors that sign BAAs, technical controls like encryption, access rules, and audit logs, and a team that uses the app responsibly.
Start with the checklist above, write down your answers, and repeat the review each time you add an AI feature. An AI app builder with these controls built in makes healthcare data protection part of the app from the first version.
{CTA button:Try CodeBlox free:https://www.codeblox.com/sign-up:Build your next healthcare app with access controls, audit logs, and approvals ready from the start.}
Find answers to the most common questions about our no-code platform and how it can help you build powerful business application solutions without writing a single line of code.
It means controlling where patient data goes when AI features use it. That covers prompts, logs, generated outputs, and any outside AI service that processes the data.
Encrypt all patient data, limit access by role, and log every action. Make sure AI providers sign BAAs and do not store or train on patient data.
It involves signed BAAs, HIPAA-eligible hosting, encryption, role-based access, multi-factor authentication, and audit logs. Teams also need a documented risk analysis and staff training before launch.
It is software that can be set up and used in a way that meets HIPAA's Privacy and Security Rules. HHS does not certify software, so compliance depends on configuration and use.
They are AI-powered apps that protect patient health information according to HIPAA rules. Every vendor that handles that data, including the AI model provider, must sign a Business Associate Agreement.

Tilly leads Operations and Solution Delivery at CodeBlox, partnering with enterprise teams to design scalable business systems before development begins. With hands-on experience across ERP, CRM, finance automation, and industry-specific digital transformation projects, she writes about solution architecture, process optimization, AI-powered workflows, and the practical decisions that determine whether enterprise software succeeds in the real world.