- Solutions
- Pricing

Most businesses ask the security question at the wrong point. They evaluate a no-code platform's features first, pick a template, start building workflows, and then ask the IT team to check if it is secure. Well, the architecture of data security in no-code platforms does not work that way.
In a no-code platform, the security is built into the stack before a single user logs in, and understanding that layered structure is what separates businesses that implement a solution confidently from those that hesitate indefinitely.
In this blog, we will explore every potential point to understand how a no-code platform handles security and access control.
No-code platform security features operate across multiple layers, working simultaneously to protect the system. And the platform handles server hardening, network firewalls, and protection against distributed attacks at the infrastructure level.
If we move up the stack, at the application layer, it manages authentication, session integrity, and input validation. Similarly, at the data layer, it enforces encryption and access rules. Importantly, each of these layers is maintained by the platform vendor rather than your internal team.
However, this multi-layered structure is truly tested through multi-tenancy isolation. In such environments, hundreds of companies can share the same underlying infrastructure, yet each company’s data remains completely invisible to others. To understand this better, here is how that separation works.
As a result, your application’s structure remains visible to the right people within your organization, while the underlying database stays completely inaccessible to anyone outside the defined permission boundaries.
Every byte that moves between a user's browser and the platform travels inside a TLS 1.3-encrypted tunnel. This ensures that data in transit remains secure at all times.
In addition to this, no-code platforms use AES-256 encryption for data stored within the system. Therefore, even if someone gains physical access to the server hardware, the data remains unreadable without the decryption key.
Beyond these two layers, field-level security introduces a third layer that is often overlooked. But it is equally important. To better understand its role, here is what that looks like:
Finally, this last point is particularly important for businesses operating in healthcare, finance, or legal sectors. In such cases, a breach at the record level does not automatically expose every sensitive field within it. Additionally, the way field-level rules interact with structured data is explored further in our guide on no-code databases.
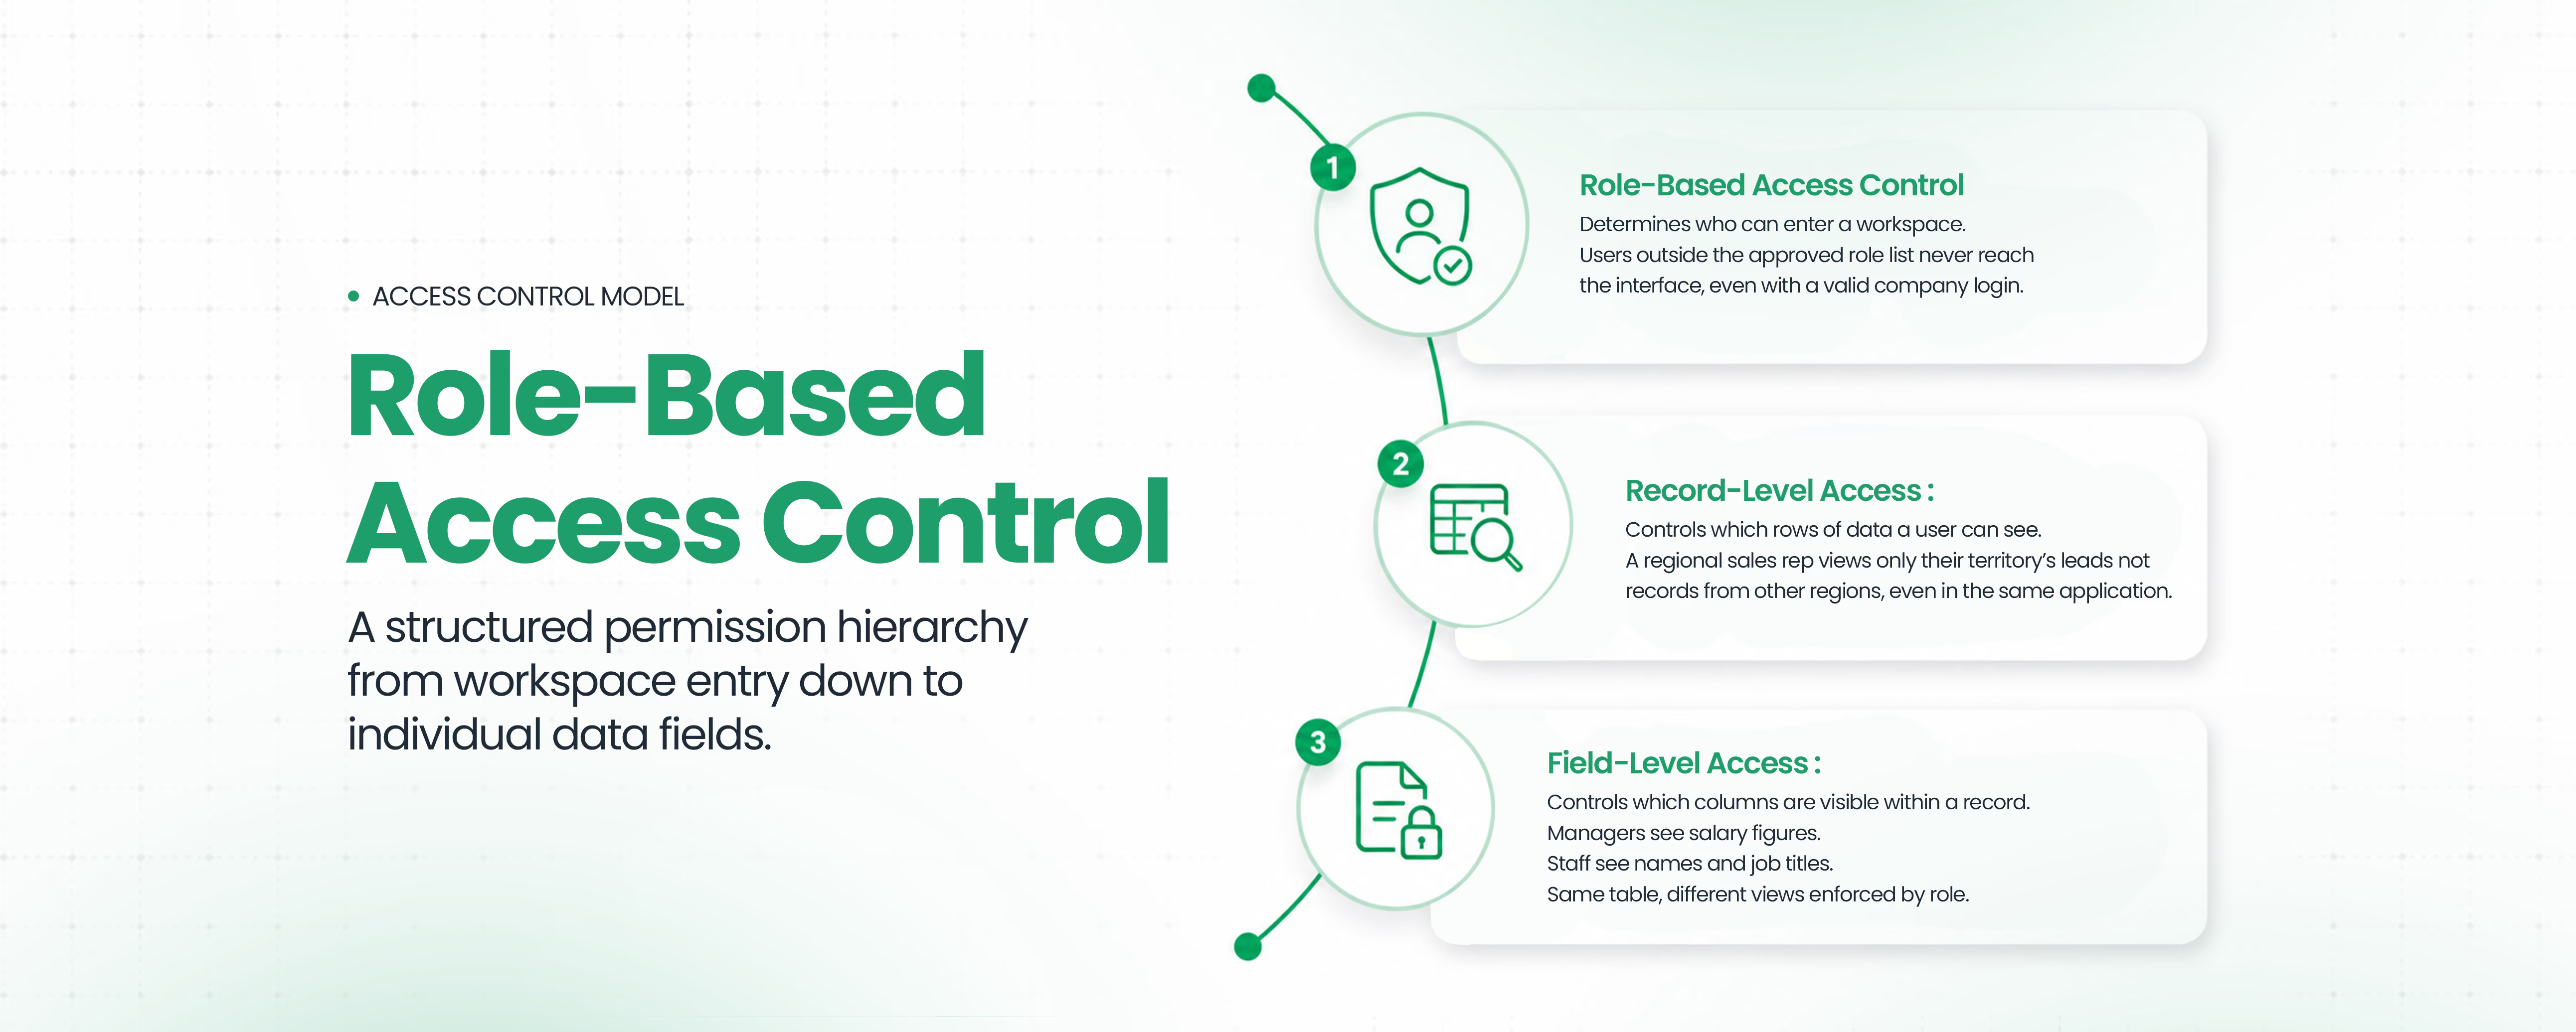
Role-based access control is a core component of data security in no-code platforms, as it determines who can access, view, and interact with data at every level of an application. In enterprise no-code security, this is not a simple on or off permission. Instead, it is a structured system designed to prevent unnecessary data exposure while ensuring users can perform their roles effectively.
Within no-code development platforms, role-based access control operates across a hierarchy of permission levels, with each level becoming more granular than the last. This layered approach ensures that access control in no-code platforms is enforced consistently across users, teams, and workflows.
To understand how this works in practice, let us look at each level more closely:
Together, these layers form a practical implementation of access control in no-code platforms, where data visibility is tightly aligned with user roles and responsibilities.
In addition to these controls, CodeBlox integrates role-based access control with identity providers such as Azure AD, Okta, and Google Workspace through Single Sign-On. This ensures that user permissions remain synchronized with organizational roles. When someone joins, changes roles, or leaves the organization, their access is updated automatically through the connected directory.
Furthermore, the 2026 IBM RBAC Implementation Guide highlights that structuring access around least-privilege principles significantly reduces the overall attack surface within an organization. This is the same principle applied across CodeBlox, where access control is designed to support enterprise no-code security without requiring manual intervention.
API security in no-code platforms does not rely on a single mechanism. The three controls work together to ensure authentication, prevent overload, and maintain accountability for every external request made to the platform.
To better understand this, let us look at how each control functions in practice:
In addition to these controls, industry insights further reinforce the importance of structured API security. The 2025 Global State of API Security report identifies broken object-level authorization as one of the most commonly exploited API vulnerabilities across industries.
However, in no-code platforms, this risk is addressed at a structural level. Since users interact through abstracted interfaces rather than writing raw queries, the platform’s query layer automatically enforces object-level permission checks on every request.
The operational difference between the two approaches becomes clearest when you look at day-to-day security maintenance rather than the initial setup. In practice, the contrast is not just technical but also operational, as it directly impacts how consistently and efficiently teams can manage risk over time.
Platforms like CodeBlox are designed to eliminate fragmented security ownership by centralizing critical security functions at the platform level. Instead of treating security as an application-specific responsibility, CodeBlox standardizes and automates it across every application built on the platform.
As the table illustrates, traditional development requires teams to handle each security responsibility independently. In contrast, no-code platforms standardize and centralize these processes.
For instance, in custom development, each application carries its own security maintenance burden. A patch involves identifying the vulnerability, writing a fix, testing it, and then deploying it separately for each application.
On the other hand, within a no-code platform, this entire cycle is managed by the vendor. As a result, the fix is implemented once at the platform level, and every application benefits from it simultaneously, without requiring any action from your team.
No-code platforms like CodeBlox are designed to simplify compliance by embedding audit-readiness directly into the system. Instead of requiring teams to build tracking mechanisms from scratch, the platform ensures that every critical action is recorded automatically.
For example, every create, read, update, and delete action inside a CodeBlox application generates an immutable log entry. As a result, these automated audit logs provide compliance teams with a complete, timestamped record of who accessed what data and when. This level of traceability is a baseline requirement for certifications such as SOC 2 Type II and ISO 27001.
Furthermore, for businesses operating in regulated industries, the platform’s existing certifications serve as a strong starting foundation rather than a blank slate. In practical terms, a healthcare company does not need to build audit-ready logging from the ground up, as much of the required structure is already in place.
In addition to this, industry research continues to validate this shift. A 2025 paper in IEEE Xplore proposes standardized governance frameworks specifically for no-code security, highlighting that the sector has matured enough to establish its own formal compliance standards alongside traditional software development.
The current generation of access control in no-code platforms is primarily rule-based. You define permissions, and the platform enforces them. That model is now evolving toward something more dynamic and responsive, and this shift is already visible in 2026 platforms.
Instead of relying only on predefined rules, modern systems are beginning to observe user behavior and respond in real time. This introduces a new layer of security that adapts as activity patterns change.
The JRD Systems 2026 enterprise development report describes AI co-creation and native data capabilities as foundational to automated threat detection. This signals a clear shift from static permissions to systems that continuously monitor and respond on their own.
Every security layer discussed in this blog, including multi-tenancy isolation, field-level encryption, RBAC, SSO integration, API authentication, immutable audit logs, and behavioral threat detection, operates beneath every application built on CodeBlox.
Your team configures access rules through a visual interface, while the underlying infrastructure requires no custom code to maintain, patch, or audit. This significantly reduces the operational burden on internal teams.
No-code does not mean security is compromised. It means the complexity of security is handled at the platform level by specialists, allowing your team to focus entirely on building workflows that drive business value. The no-code platforms guide goes into more detail about how no-code platforms facilitate scalable operations.
If you're planning to build secure, scalable applications without managing security complexity manually, this is where CodeBlox makes a difference.
{CTA button:Book a Demo with CodeBlox:https://www.codeblox.com/schedule-demo}
Find answers to the most common questions about our no-code platform and how it can help you build powerful business application solutions without writing a single line of code.
Data security in no-code platforms is ensured through a multi-layered defense-in-depth strategy. Leading no-code platforms bake protection directly into the infrastructure using TLS 1.3 for data in transit and AES-256 for data at rest. By automating no-code platform security features like encryption and audit logging, these tools eliminate the human error often found in manual coding.

Tilly leads Operations and Solution Delivery at CodeBlox, partnering with enterprise teams to design scalable business systems before development begins. With hands-on experience across ERP, CRM, finance automation, and industry-specific digital transformation projects, she writes about solution architecture, process optimization, AI-powered workflows, and the practical decisions that determine whether enterprise software succeeds in the real world.